When software can reach into the physical world, small lapses compound into big losses; the French supermarket freezer hack made that painfully concrete by turning routine remote controls into a nationwide spoilage event.
At a Glance
- French authorities opened a criminal probe into a large-scale cyberattack that manipulated connected refrigeration across several major retail chains.
- The prime minister’s office tasked ANSSI, France’s cyber agency, to investigate and coordinate with European counterparts.
- Early focus centers on Danfoss refrigeration controllers, particularly legacy AK-SM800/AK-SC355 lines running outdated firmware.
- Patterns of abnormal heating, food losses, and isolated fires align with remote manipulation of operational-technology controls.
What happened and why it matters beyond groceries
French prosecutors confirmed a formal investigation into a “large-scale” cyberattack that affected connected refrigerators at multiple leading supermarket groups, with reports of devices driven to abnormal temperatures, spoiled perishables, and some fire incidents. Prosecutors characterized the case as a cyberattack rather than routine equipment failure and assigned it to the anti-cybercrime section; OFAC investigators were tasked with identifying victims and linking losses to the attack. In parallel, the prime minister’s office directed ANSSI—the national cybersecurity agency—to lead the technical inquiry and liaise with European partners, a signal that the government sees systemic risk extending beyond one vendor or chain.
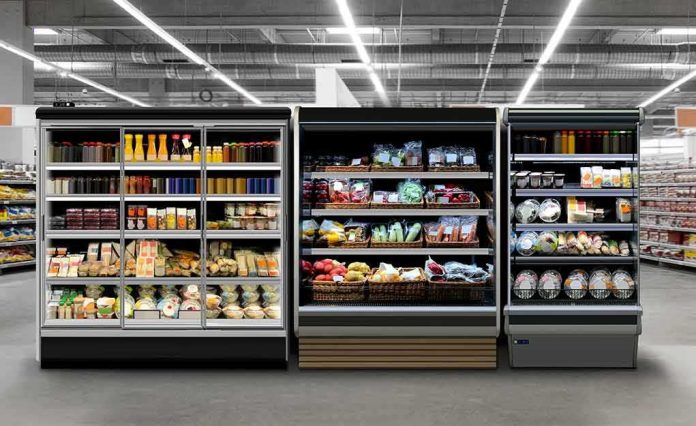
This was not an IT nuisance about screens and email. Refrigeration is operational technology: networked control of compressors, thermostats, and defrost cycles that keep the cold chain intact. Disrupt it and consequences are physical—food warms, pathogens bloom, inventory is discarded, and in edge cases electrical stress can contribute to hazardous conditions. That is precisely the posture investigators described, and it aligns with accounts from retailers who disabled remote access and shifted to manual control to stop the damage cascade.
The technical spine: controllers, connectivity, and failure modes
Early reporting isolated a common equipment denominator: Danfoss supervisory controllers, notably the AK-SM800 and AK-SC355 lines. A version of the AK-SM800 implicated in affected sites was reportedly running outdated firmware, expanding the attack surface. Danfoss acknowledged “incidents in France affecting a limited number” of refrigeration management systems and explicitly tied impacted units to outdated firmware; the company said it had urged customers to update supported systems and migrate legacy ones.
How could an attacker turn cold cases hot? In supermarket installations, supervisory controllers orchestrate setpoints, scheduling, alarms, and defrost logic across dozens of cases. An adversary who gains authenticated access—whether by exploiting an exposed management interface, default credentials, weak remote-access gateways, or a software flaw—can raise setpoints, force defrost cycles, suppress alarms, and alter schedules. Across hundreds of stores, subtle manipulation (a few degrees here, a defrost extended there) compounds into overnight spoilage. The pattern described publicly—coordinated abnormal heating across chains—fits remote manipulation of OT controls far more closely than coincident mechanical failures.
How we got here: OT convenience outpacing OT security
Supermarket refrigeration modernized for good reasons: energy optimization at fleet scale, predictive maintenance, and fewer midnight truck rolls. That required connectivity. But the security model of many OT estates still trails enterprise IT. Patch windows are scarce; legacy controllers run long past vendor support; remote-access paths multiply; segmentation is inconsistent. Government and industry case studies have catalogued this delta for years: when industrial control systems are connected and under-governed, cyber incidents spill into the physical world, from grid operations to safety systems to process controllers. The food sector is no exception; European analyses have specifically flagged refrigerated logistics and storage as high-probability, high-impact cyber targets because a few hours of temperature abuse cascades into immediate spoilage and costly disposal.
That context makes the French episode unsurprising in mechanism even if striking in scale. It also explains why the prime minister’s office put ANSSI on point and initiated coordination with European peers—refrigeration OEMs, integrators, and retailers operate across borders and often share architectures and service providers.
What the evidence supports—and what it does not claim
On the record, three elements are solid. First, law enforcement and specialized cyber units are treating the disruptions as a coordinated attack with real-world losses, not a maintenance mishap. Second, the government assigned ANSSI to the technical investigation, elevating it beyond private incident response to a national concern. Third, Danfoss confirmed incidents in France involving refrigeration-management systems running outdated firmware and reiterated its guidance to update or replace legacy controllers.
There is, appropriately, restraint around the intrusion chain and attribution. Public reporting to date has not named a perpetrator or motive, and investigators have not released forensics detailing the precise access vector. That caveat does not diminish the central facts of the incident; it is normal investigative sequencing in OT cases where device seizure, controller imaging, and log correlation take time.
Operational lessons for retailers and suppliers
Three practice areas separate resilient supermarkets from soft targets. First, lifecycle discipline: unsupported supervisory controllers must be retired on a schedule as firm as food-safety rotation charts. “Outdated firmware” is not an abstract risk when the device governs compressors and defrost cycles that protect inventory; Danfoss’s own advisory underscores the point. Second, access control and segmentation: management portals and field-bus gateways belong behind properly authenticated, monitored remote-access solutions, with store-level networks segmented from enterprise IT and the public internet. Industry assessments have repeatedly shown how often control interfaces are left reachable—sometimes directly from the internet—creating an easy beachhead.
Third, independent telemetry and alarms: temperature sensors that log to a separate channel—SMS out-of-band alerts, cellular-backed gateways, or mechanical high-temp alarms—create a backstop when a supervisory controller is subverted. In this incident, the overnight timing multiplied losses; independent alerting can shrink time-to-detection from hours to minutes and turn a mass spoilage into a few pallets written off.
Government’s role: from incident response to sector hygiene
ANSSI’s remit in this case should not end with a technical after-action. Food retail is a critical service whose margins and franchised ownership models often push security upgrades down the road. Sector-specific guidance, minimum baselines for remote-management exposure, and structured disclosure from OEMs on support sunsets can reset incentives. The pattern is familiar in OT-heavy sectors: when regulators and national cyber agencies set clear expectations and back them with procurement levers and insurance alignment, patch levels rise, remote access hardens, and common exposures recede. Coordination with European counterparts matters here because vendor fleets, managed-service providers, and franchise operators span borders; consistent expectations reduce weakest-link effects.
Why this is a bellwether for connected infrastructure
The French freezer hack belongs to the same family as prior OT compromises that reached into the physical domain—even if the sector and stakes differ. The through-line is simple: when convenience, centralization, and remote reach are designed without equal attention to lifecycle support, network boundaries, and human oversight, an attacker can turn the very features buyers value into levers for disruption. The remedy is not retreat from connectivity but disciplined engineering and governance: supported devices, defended pathways, independent failsafes, and rehearsed incident response. The alternative is to keep learning the hard way—one overnight spoilage, one darkened facility, one avoidable fire at a time.
Major French supermarket chains hit by cyberattack, causing refrigerators to shoot up in temperature https://t.co/7BIwtqLxY0
— CTV National News (@CTVNationalNews) October 13, 2026
Sources:
townhall.com, dw.com, afp.com, france24.com, insurancebusinessmag.com, timeslive.co.za, tab-beim-bundestag.de